Vercel Sandbox now supports Secure Compute
Vercel Sandbox now integrates Secure Compute, enabling sandboxes to connect to a team’s private network and access restricted resources via AWS VPC peering.
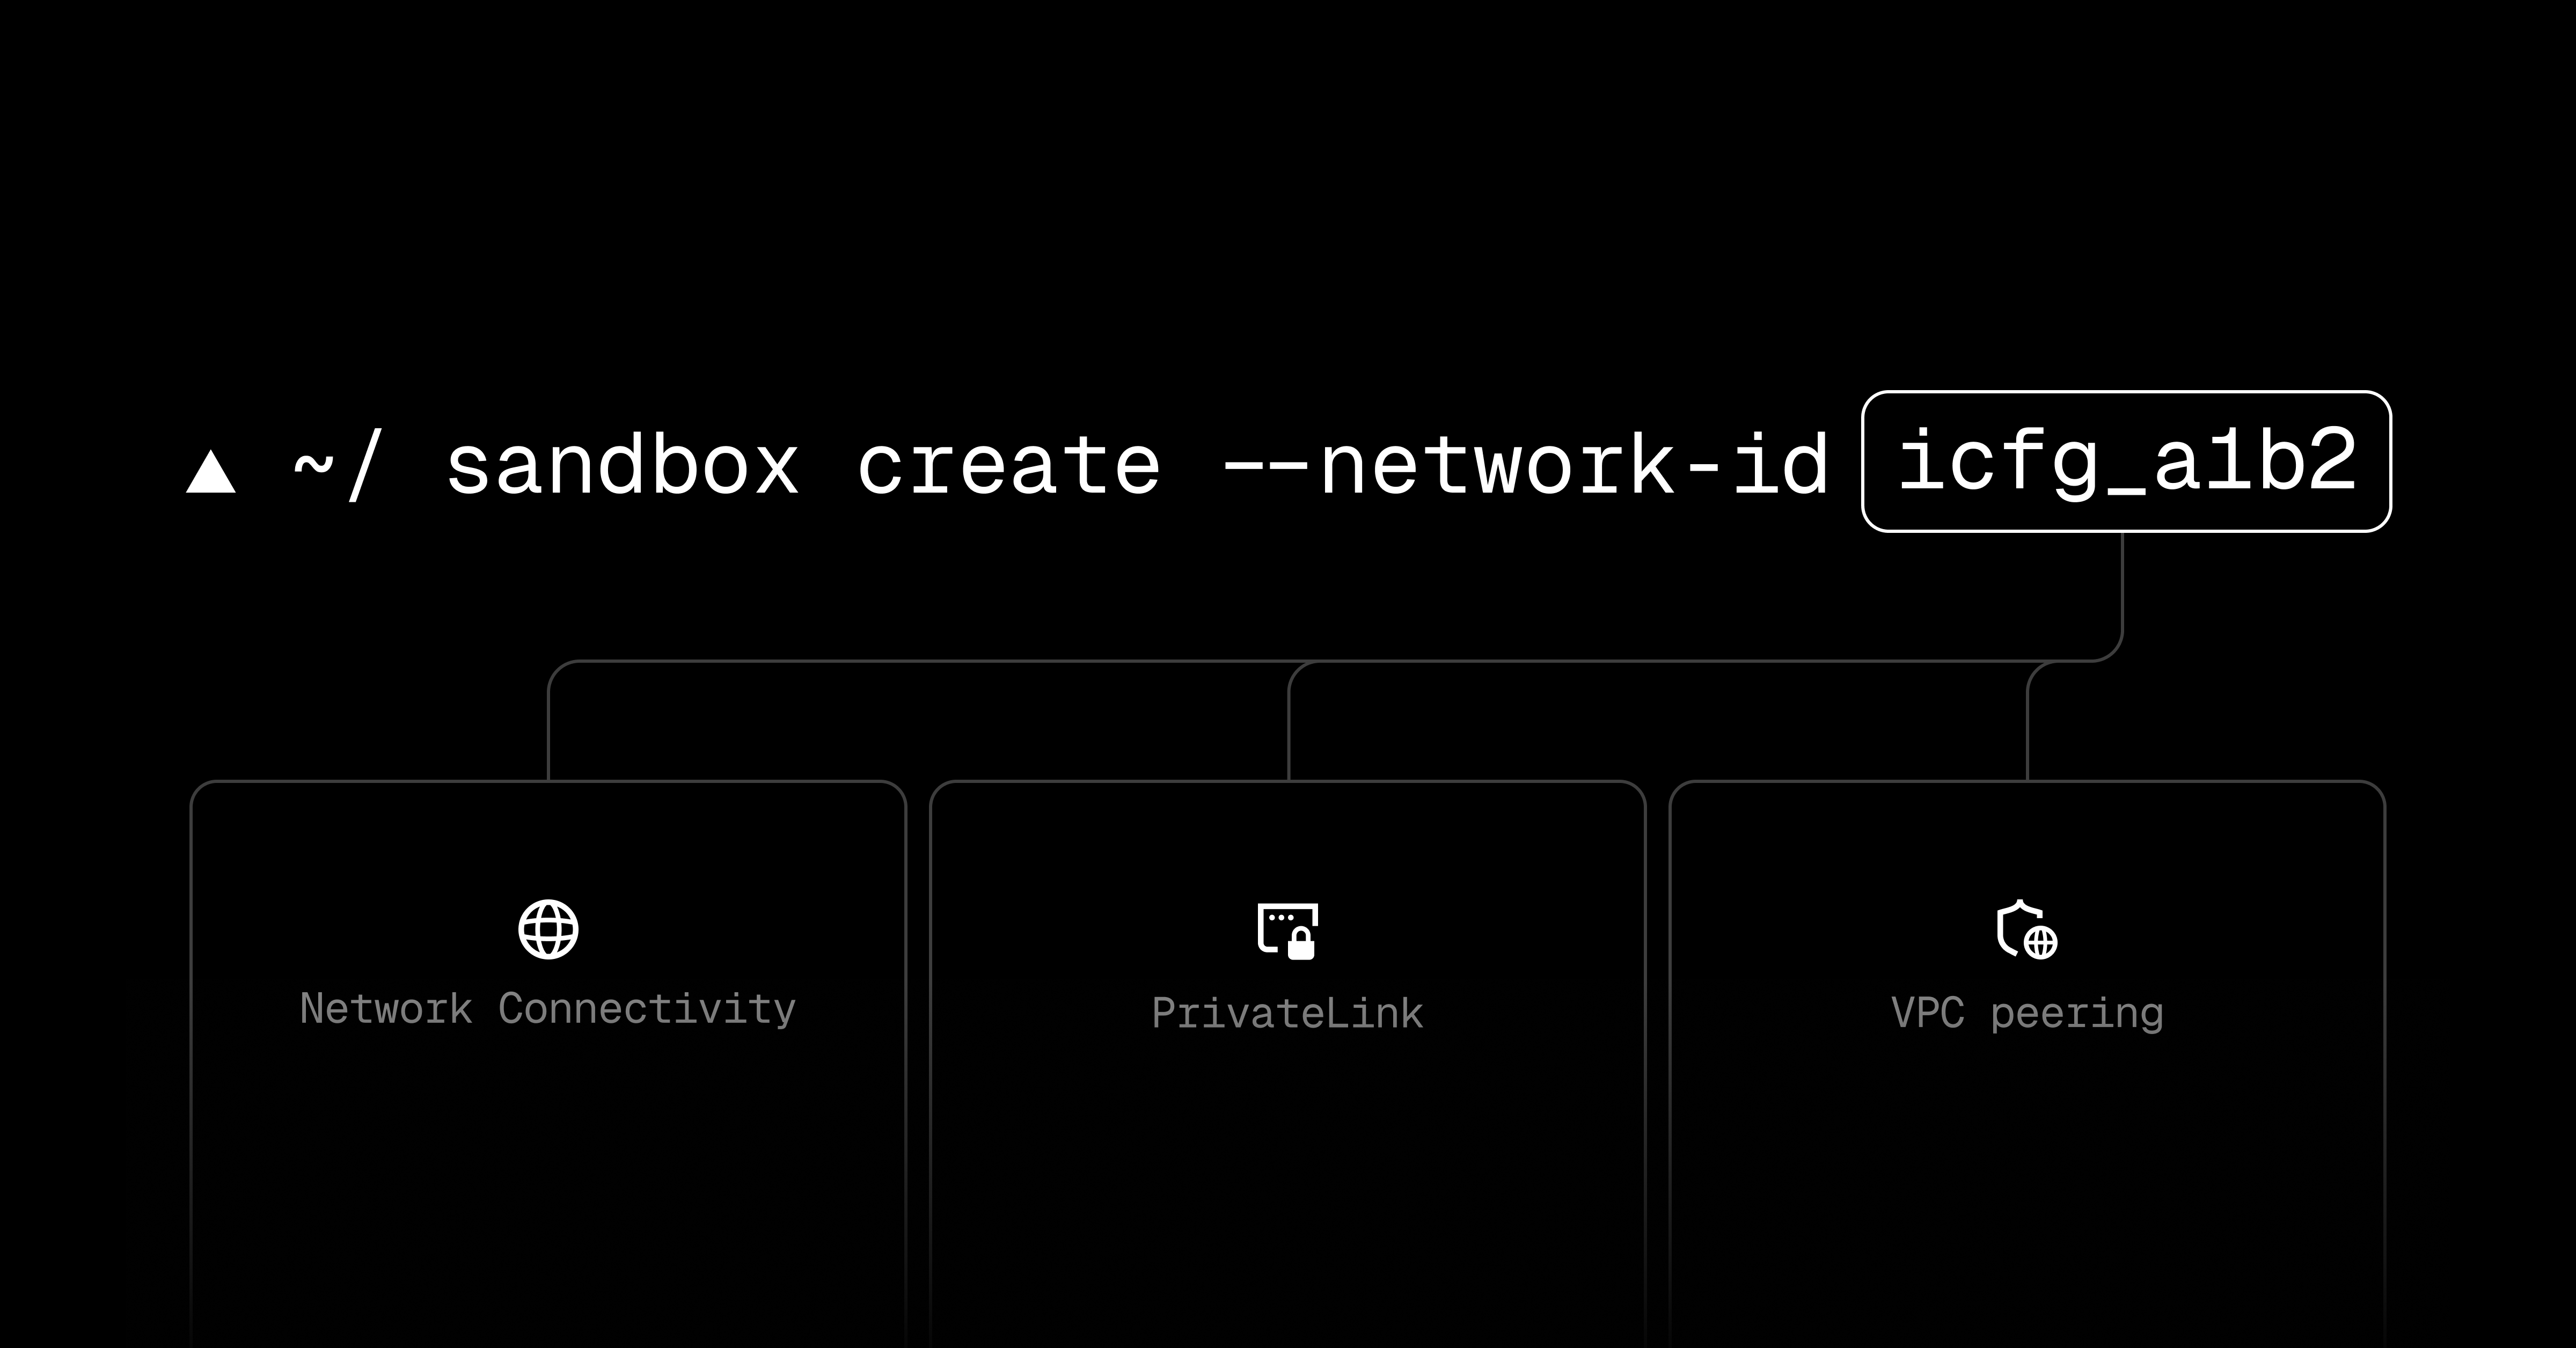
Vercel Sandbox has introduced Secure Compute, allowing sandboxes to link to a team’s dedicated network. Public traffic from sandboxes exits through the network’s static IPs, enhancing control over outbound connections. Sandboxes can also access private resources within an AWS VPC through VPC peering, expanding their operational scope. This feature is designed to improve security and resource access for development environments.
Teams can attach a sandbox to their network either programmatically in code or via the Vercel CLI. The integration supports dynamic network attachment, enabling teams to modify sandbox networks as needed. Changes take effect at the start of the next session, ensuring minimal disruption to ongoing work. Existing sandboxes can update their network settings using the sandbox.update() method.
The Secure Compute feature is currently available exclusively to Enterprise teams. It requires explicit configuration to ensure proper network routing and security policies. Teams must enable Secure Compute in their Vercel project settings to utilize this functionality. This targeted availability ensures the feature meets enterprise-grade security and compliance standards.
A running sandbox session retains its current network configuration until it is stopped. This behavior prevents abrupt disruptions during active development cycles. Once stopped, the sandbox will adopt the newly configured network upon restart. This design prioritizes stability while allowing teams to adapt their network settings as requirements evolve.